Photo: Illustrative
Aave Founder Says V3 Is Safe After $305K Third-Party Adapter Exploit
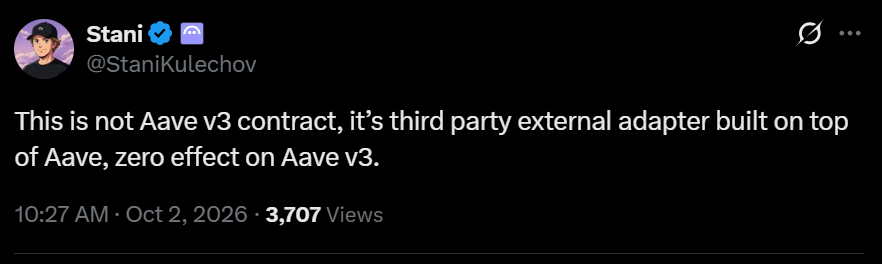
Aave founder Stani Kulechov said Aave v3 was not hit by an exploit that drained about $305,000 from two Safe multisig wallets. In a post on X, he explained that the attack targeted a third party external adapter built on top of Aave, not the v3 contract itself, so the protocol saw zero effect. Security firm SlowMist did not report any losses to Aave v3 itself.
.jpeg)
Aave founder Stani Kulechov said Aave v3 was not hit by an exploit that drained about $305,000 from two Safe multisig wallets. In a post on X, he explained that the attack targeted a third party external adapter built on top of Aave, not the v3 contract itself, so the protocol saw zero effect. Security firm SlowMist did not report any losses to Aave v3 itself.
How the Safe Multisig Wallets Were Drained
SlowMist said the attack went after a module used to open and close leveraged Aave v3 positions through Safe wallets. The attacker abused an access control flaw that let a fake Safe contract pass the adapter’s authorization check. The adapter also let the caller control the router and transaction data used for swaps, which the attacker used to run transactions through the victim Safes and pull out weETH and collateral.
FlashLoopAdapter Vulnerability and Stolen Funds
During the attack, around 1,300 wrapped Ether (WETH) of debt was repaid to unlock collateral. In the end, the attacker took about 114.09 Ether (ETH), worth roughly $305,000, from the two Safe multisigs. SlowMist identified the vulnerable FlashLoopAdapter contract along with the attacker’s wallet.
Live market reaction
Disclaimer
This content is for informational purposes only and does not constitute financial, investment, or legal advice. Cryptocurrency trading involves risk and may result in financial loss.
Start trading
with BloFin today
Up to $500 sign-up bonus and zero-fee trading on your first 30 days.
Buy crypto nowⓘ You will be redirected to BloFin
About the author
Emerging voice in crypto journalism with a background in fintech and digital economics. Covers DeFi, NFTs, and the evolving regulatory landscape.
 Tristan R. ·
 Laurisa ·