Photo: Illustrative
Initia Blames Stolen Cloud Key for Second Breach in Three Weeks
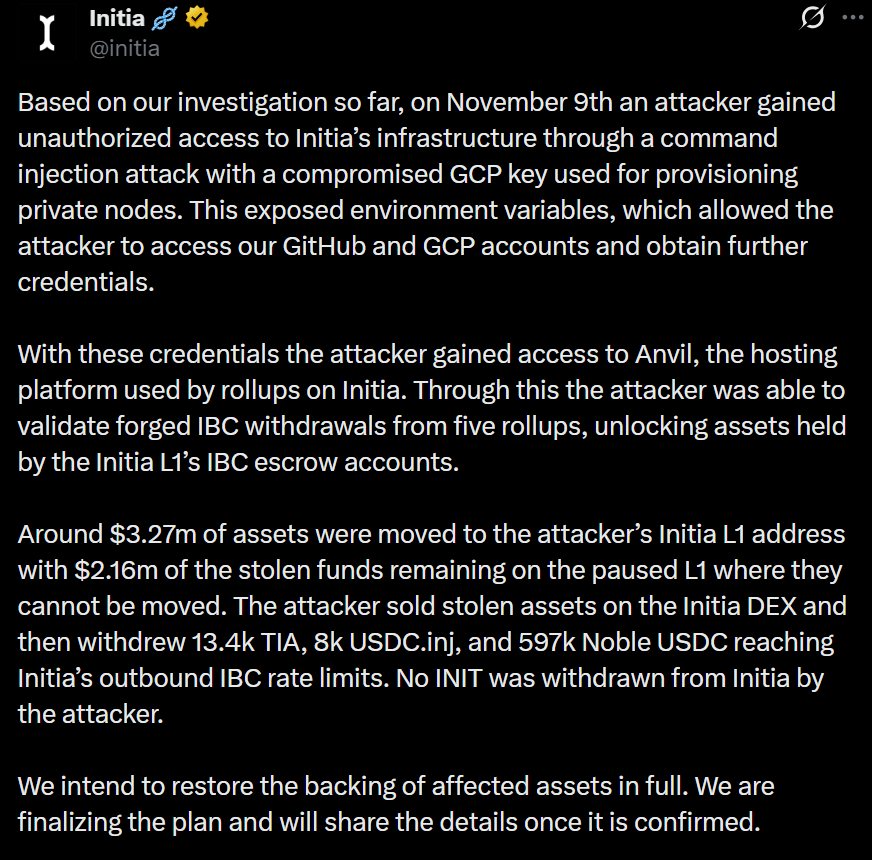
Initia says an attacker got in on Monday by abusing a command injection flaw tied to a compromised Google Cloud Platform key. That opened up environment variables, which gave the intruder a path into the project's GitHub and cloud accounts and let them pick up more credentials. With that access, the attacker reached Anvil, the platform that hosts Initia's rollups, and approved fake IBC withdrawals from five rollups, draining assets from the network's escrow accounts.
Initia says an attacker got in on Monday by abusing a command injection flaw tied to a compromised Google Cloud Platform key. That opened up environment variables, which gave the intruder a path into the project’s GitHub and cloud accounts and let them pick up more credentials. With that access, the attacker reached Anvil, the platform that hosts Initia’s rollups, and approved fake IBC withdrawals from five rollups, draining assets from the network’s escrow accounts.
What the Attacker Took and What Remains Frozen
The thief sold assets on Initia’s own decentralized exchange and pulled out 13,400 TIA, 8,000 USDC.inj and 597,000 Noble USDC. No INIT tokens left the network. About $2.16 million of the stolen funds is still frozen on the halted chain.
Initia Halts the Chain and Starts Recovery
The team stopped its layer-1 on Tuesday and says it plans to restore the backing of the affected assets. Recovery work continues alongside law enforcement and security partners.
Earlier Exploit on Oct. 23
This is not the first incident. On Oct. 23, an attacker drained roughly $2.7 million through a weakness in the MoveVM script cache, which let malicious code skip security checks and mint unbacked token balances that were then bridged out.
Live market reaction
Disclaimer
This content is for informational purposes only and does not constitute financial, investment, or legal advice. Cryptocurrency trading involves risk and may result in financial loss.
Start trading
with BloFin today
Up to $500 sign-up bonus and zero-fee trading on your first 30 days.
Buy crypto nowYou will be redirected to BloFin
About the author
8+ years covering crypto markets, macro, and geopolitics. Previously at Decrypt and CoinDesk. Focused on the intersection of digital assets and traditional finance.
Houthis Claim Ballistic Missile Attack on Riyadh Airport and Financial Centre
 Laurisa ·
Bitcoin Plunges to a Three Month Low Near $62,080 as Analyst Spots a Fourth Capitulation Wave
Laurisa · 
Nearly 1,500 Migrants Reach the Canary Islands in a Single Day, the Highest Since 2020
 Tristan R. ·