Photo: Illustrative
Weak Certificate Keys at eMudhra Force Urgent Teku and Besu Updates
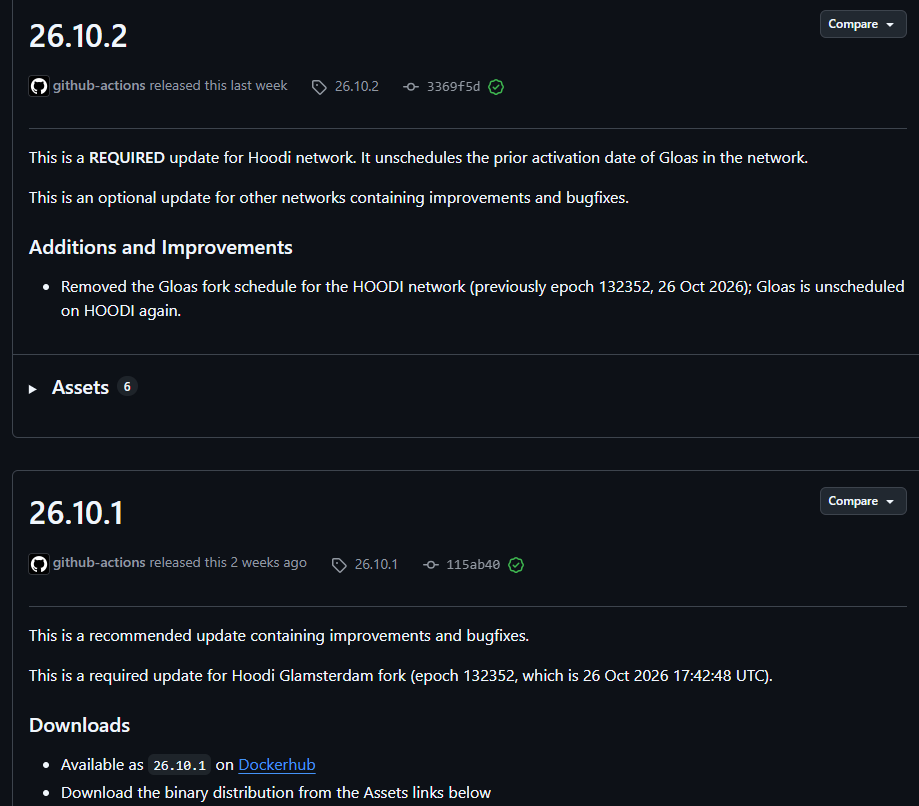
A cryptography mistake at eMudhra, an Indian certificate authority, has pushed two major Ethereum clients to release fixes. Teku shipped version 26.10.3 on Tuesday and Besu released 26.10.2 on Monday, and both Docker images now refuse to trust certificates linked to the company. Left unpatched, some setups could have let attackers quietly redirect block rewards to their own addresses. No exploitation has been reported, and Teku says a default mainnet node is not affected.
.jpeg)
A cryptography mistake at eMudhra, an Indian certificate authority, has pushed two major Ethereum clients to release fixes. Teku shipped version 26.10.3 on Tuesday and Besu released 26.10.2 on Monday, and both Docker images now refuse to trust certificates linked to the company. Left unpatched, some setups could have let attackers quietly redirect block rewards to their own addresses. No exploitation has been reported, and Teku says a default mainnet node is not affected.
What Went Wrong With the Certificate Keys
On Oct. 17, researchers found that private keys for eight of eMudhra’s intermediate certificate authorities were created with too little randomness. Because the keys could be worked out from public certificates, anyone could issue fake ones that unpatched software would accept. Browsers blocked them, eMudhra revoked them a day later, and the company has said it will leave the certificate business. Java does not check revocation by default, so Teku’s Docker images kept trusting the bad certificates.
What Node Operators Need to Do
People running Teku or Besu without Docker must update Java themselves, since the client update does not change Java’s trusted certificate list. The new Docker images also do not fix Java on the host machine. Operators on Java 26 face a harder path, because that version is end of life and will get no patch, so they need to move to Java 25.
Live market reaction
Disclaimer
This content is for informational purposes only and does not constitute financial, investment, or legal advice. Cryptocurrency trading involves risk and may result in financial loss.
Start trading
with BloFin today
Up to $500 sign-up bonus and zero-fee trading on your first 30 days.
Buy crypto nowYou will be redirected to BloFin
About the author
Emerging voice in crypto journalism with a background in fintech and digital economics. Covers DeFi, NFTs, and the evolving regulatory landscape.
 Laurisa ·
 Guylian ·
 Tristan R. ·